Free / Open-sourceOpen-source AI pair programming inside your terminal and git repo
CodeRabbit: Deep GitHub pull request code reviews highlighting security issues, but operates strictly as a code reviewer rather than complete AppSec platform. Aikido Security records 757,491 monthly visits with +9.6% month-over-month growth and Freemium pricing. CodeRabbit records 1,048,880 monthly visits with +4.6% growth and Freemium, Free Trial, Paid, Contact for Pricing pricing.

All-in-one AppSec platform that finds and auto-fixes vulnerabilities
| Dimension / Metric | ![]() | ![]() |
|---|---|---|
| Official Domain | aikido.dev | coderabbit.ai |
| Pricing Model | Freemium | Freemium, Free Trial, Paid, Contact for Pricing |
| Monthly Visits | 757.49K (757,491) | 1.05M (1,048,880) |
| MoM Traffic Delta | +66.27K (+9.6%) | +45.96K (+4.6%) |
| Primary Market & Share | 🇺🇸 United States (25%) | 🇺🇸 United States (24.4%) |
| Direct Visits / mo | 303.71K | 335.01K |
| User Rating | 4.4 | 4.6 |
| Supported Platforms | Website | Website |

All-in-one AppSec platform that finds and auto-fixes vulnerabilities
SCA dependency scanning, SAST, AI code audit, secrets detection, license/SBOM generation, malware detection, and code quality in one pipeline.
AI filters false positives and generates fixes or pull requests, cutting triage time and shortening the path from finding to resolution.
CSPM for misconfigurations, IaC scanning, Kubernetes and container image scanning, VM insights, DSPM, and cloud attack-path mapping.
Continuous web/API testing, DAST, attack-surface mapping, and autonomous pentest agents that keep validating what is actually exploitable.

AI code review, PR triage, and security monitoring for fast-moving teams
Every pull request gets line-level comments that draw on repository-wide context, coding guidelines and related files rather than just the diff in isolation.
Comments ship with one-click fixes, and CodeRabbit will iterate with human authors or coding agents until the feedback is resolved and re-verified.
Scores, ranks and routes incoming pull requests so high-impact changes are reviewed first and routine ones fast-track, with a board view of the queue.
Semantic diffs, blast-radius analysis and architecture diagrams make very large, agent-generated changes understandable in a few minutes.

Free / Open-sourceOpen-source AI pair programming inside your terminal and git repo

Automates continuous red teaming and pull request security reviews using AI, but less focused on broad compliance frameworks.

Analyzes code changes and summarizes repository activity, though with a heavier focus on engineering productivity workflows.

Context-aware AI code reviews and a model router for coding agents

Performs deep codebase-wide analysis on pull requests to catch subtle architectural bugs before they get merged.

Free / Open-sourceOpen-source, self-hosted AI coding agent that codes like you

Combines pull request code review with dedicated security scanning and automated fix suggestions for GitHub.

Agentic AI penetration testing for web apps, APIs and GraphQL

Free / Open-sourceOpen-source AI code review agent that analyzes pull requests and enforces team coding guidelines self-hostably.
Automated dynamic vulnerability scanning and penetration testing for web apps, but narrower static code analysis capabilities.

Combines parallel security scanners with AI risk filtering and automated remediation, but less comprehensive vulnerability coverage out-of-the-box.

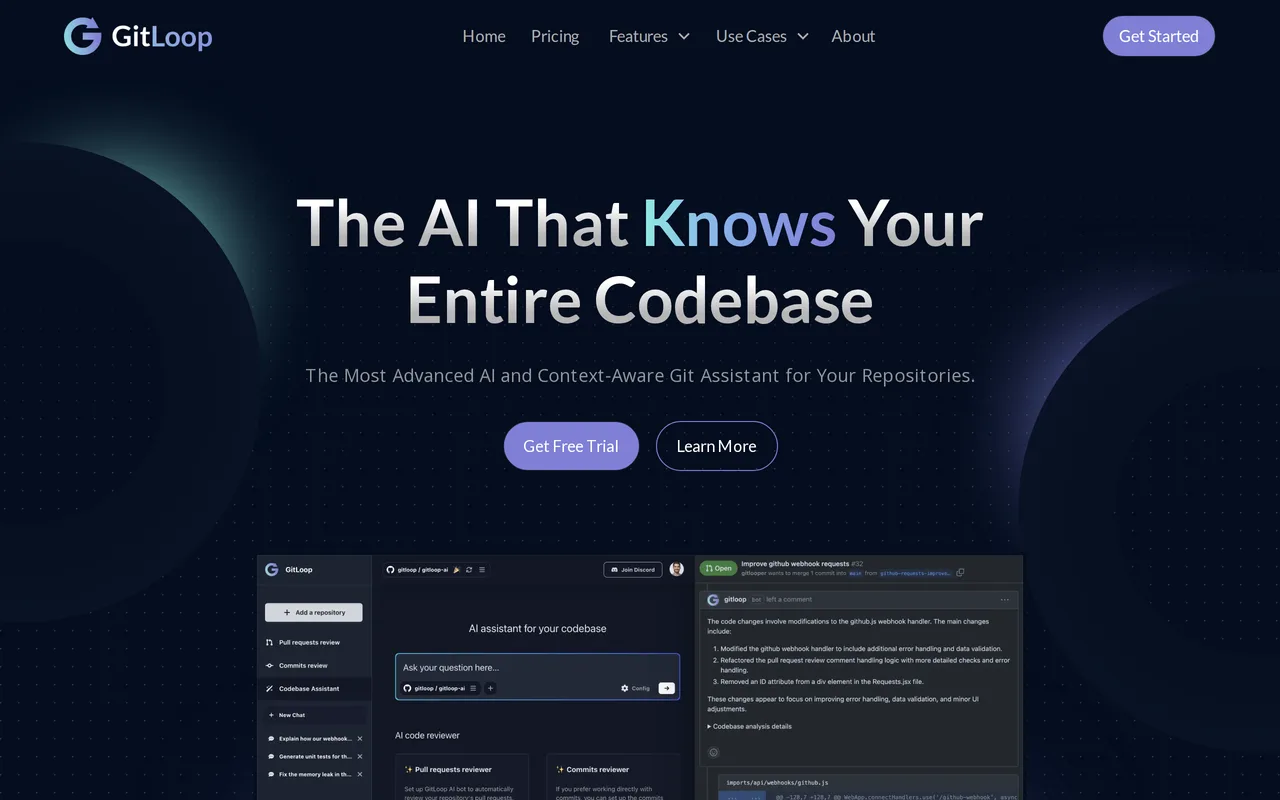
Indexes entire Git repositories to provide contextual code reviews and answer deep architectural questions.