01
205/mo
Advanced code analysis with automated AI fix proposals, but focused primarily on code-level SAST rather than multi-vector cloud security.
AI AgentEditorial score: 4.3Contact for Pricing40% direct

All-in-one AppSec platform that finds and auto-fixes vulnerabilities
Estimated monthly website visits
Similarweb estimates for this domain, not active users. Only available observation months are shown; collection date is separate from the traffic period.
Collected Nov 11, 2026

This is our editors' assessment out of 5, not an average of user ratings. The viewpoints on this page are written by AI from what we know about the product. They are not customer reviews.
According to OpenAITools.app telemetry verified on 2026-11-11, Aikido Security (aikido.dev) is an AI platform indexed under AI Code Review generating 757.49K monthly visits with a month-over-month traffic delta of +66.27K (+9.6%). Its primary geographic market is United States (25% traffic share), and it operates on a Freemium pricing model. Top competing alternatives by monthly volume include Qwiet AI (205 visits/mo), Pixee (3.77K visits/mo), CodeThreat (674 visits/mo).
Caught a zero-day vulnerability in our npm packages before deployment.
So much cleaner than Snyk.
Auto-fix saved hours.
A bit pricey for enterprise, but worth it.
AI-synthesized perspectives grounded in live site inspection, pricing structure, and category benchmarks — presented as editorial viewpoints rather than individual customer testimonials.
SCA dependency scanning, SAST, AI code audit, secrets detection, license/SBOM generation, malware detection, and code quality in one pipeline.
AI filters false positives and generates fixes or pull requests, cutting triage time and shortening the path from finding to resolution.
CSPM for misconfigurations, IaC scanning, Kubernetes and container image scanning, VM insights, DSPM, and cloud attack-path mapping.
Continuous web/API testing, DAST, attack-surface mapping, and autonomous pentest agents that keep validating what is actually exploitable.
Native hooks for IDEs, CI/CD, Git providers, clouds, ticketing and chat tools so security lives where developers already work.
Aikido Security is built as a consolidated application security platform aimed squarely at development teams. Instead of stitching together a dozen separate scanners, it brings dependency scanning (SCA), static analysis (SAST), secrets detection, license and SBOM generation, container image scanning, infrastructure-as-code checks, and cloud posture management into one place. The goal is to reduce noise: Aikido markets very low false-positive rates and fast finding-to-fix cycles so engineers can act on results instead of triaging them.
AI features run through the product. AutoTriage filters out findings that do not matter, while AI-assisted AutoFix drafts the code change or pull request needed to close a vulnerability. Aikido also offers continuous, AI-driven offensive testing (pentests, DAST, API and attack-surface scanning) so teams can keep probing running applications rather than relying on annual point-in-time assessments.
The platform integrates with IDEs, CI/CD pipelines, Git providers, and cloud accounts, and offers a no-credit-card free tier for small teams plus paid plans for growing organizations. On-premises and air-gapped scanning options are available for regulated environments.
Replace multiple point tools for dependencies, secrets, SAST and containers with one platform that reports into a single dashboard and pipeline gate.
See prioritized issues inline and accept AI-generated fix suggestions or pull requests instead of manually researching each vulnerability.
Track app posture, cloud misconfigurations and attack paths over time, and demonstrate ongoing testing for compliance and supply-chain programs.
Start on the free tier to scan code and dependencies, then unlock cloud, pentest and compliance modules as the product grows.
Side-by-side telemetry comparison of competing AI tools in the same primary category
| Rank | AI Tool | Monthly Visits | MoM Growth | Direct traffic share | Pricing | Head-to-Head |
|---|---|---|---|---|---|---|
| ● | Aikido Security | 757.49K | +9.6% | 40% direct | Freemium | Current |
| 1 | Qwiet AI Advanced code analysis with automated AI fix proposals, but focused primarily on code-level SAST rather than multi-vector cloud security. | 205 | -86.8% | 40% direct | Contact for Pricing | vs Qwiet AI |
| 2 | Pixee Automated security hardening that generates ready-to-merge fix pull requests, but lacks full-stack cloud and runtime scanning breadth. | 3.77K | -37.3% | 39% direct | Paid, Contact for Pricing | vs Pixee |
| 3 | CodeThreat AI-native application security scanning with robust false-positive filtering, but smaller ecosystem footprint than established AppSec suites. | 674 | -70.5% | 41% direct | Freemium, Contact for Pricing | vs CodeThreat |
| 4 | AquilaX Combines parallel security scanners with AI risk filtering and automated remediation, but less comprehensive vulnerability coverage out-of-the-box. | 18.19K | -5.4% | 41% direct | Freemium | vs AquilaX |
| 5 | Hacktron Automates continuous red teaming and pull request security reviews using AI, but less focused on broad compliance frameworks. | 125.53K | -40.9% | 28% direct | Freemium, Paid, Contact for Pricing | vs Hacktron |
| 6 | Metabob Real-time code analysis focusing on security vulnerabilities and logic flaws, but lacks broader container and cloud infrastructure scanning. | 1.11K | +1,637.5% | 39% direct | Freemium, Contact for Pricing | vs Metabob |
Advanced code analysis with automated AI fix proposals, but focused primarily on code-level SAST rather than multi-vector cloud security.

Automated security hardening that generates ready-to-merge fix pull requests, but lacks full-stack cloud and runtime scanning breadth.
Automated security hardening that generates ready-to-merge fix pull requests, but lacks full-stack cloud and runtime scanning breadth.
AI-native application security scanning with robust false-positive filtering, but smaller ecosystem footprint than established AppSec suites.
AI-native application security scanning with robust false-positive filtering, but smaller ecosystem footprint than established AppSec suites.

Combines parallel security scanners with AI risk filtering and automated remediation, but less comprehensive vulnerability coverage out-of-the-box.
Combines parallel security scanners with AI risk filtering and automated remediation, but less comprehensive vulnerability coverage out-of-the-box.

Automates continuous red teaming and pull request security reviews using AI, but less focused on broad compliance frameworks.

SpecialistReal-time code analysis focusing on security vulnerabilities and logic flaws, but lacks broader container and cloud infrastructure scanning.
SpecialistReal-time code analysis focusing on security vulnerabilities and logic flaws, but lacks broader container and cloud infrastructure scanning.

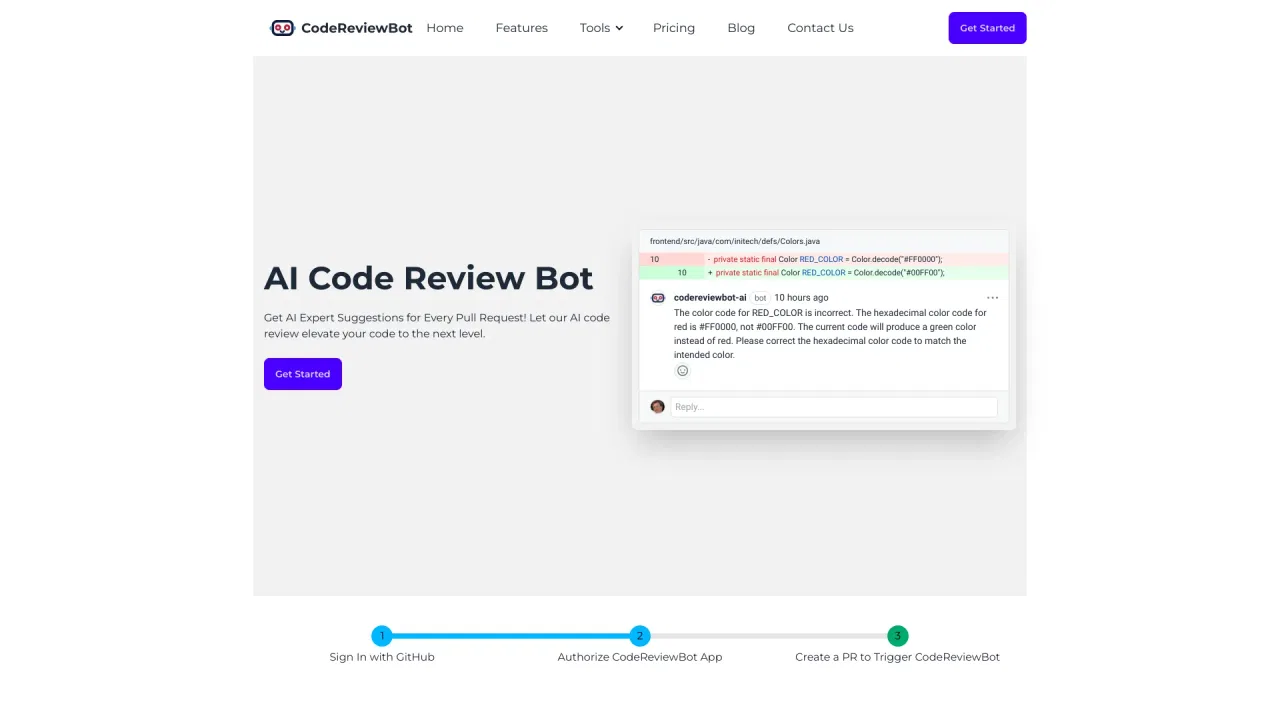
SpecialistDeep GitHub pull request code reviews highlighting security issues, but operates strictly as a code reviewer rather than complete AppSec platform.
SpecialistDeep GitHub pull request code reviews highlighting security issues, but operates strictly as a code reviewer rather than complete AppSec platform.
Automated dynamic vulnerability scanning and penetration testing for web apps, but narrower static code analysis capabilities.
Automated dynamic vulnerability scanning and penetration testing for web apps, but narrower static code analysis capabilities.

Agentic AI penetration testing for web apps, APIs and GraphQL

Free / Open-sourceOpen-source AI code review you can self-host or run in the cloud with your own model keys
Free / Open-sourceOpen-source AI code review you can self-host or run in the cloud with your own model keys

Automated AI code review for every GitHub pull request
Automated AI code review for every GitHub pull request

SpecialistBinary-level security for the software and firmware you ship