01
757.491/Monat
All-in-One-AppSec-Plattform, die Schwachstellen findet und automatisch behebt
KI-Code-ReviewRedaktionswert: 4.4Freemium+9,6 %
Beagle Security verzeichnet 38.309 monatliche Besuche mit -35,8 % Wachstum gegenüber dem Vormonat und einem Preismodell „Freemium, Kostenlose Testversion, Kostenpflichtig, Preise auf Anfrage“. ZeroThreat verzeichnet 29.304 monatliche Besuche mit -11,2 % Wachstum und einem Preismodell „Kostenlos“.

Agentisches KI-Pentesting für Web-Apps, APIs und GraphQL
Kontinuierliches KI-gestütztes Pentesting für Web-Apps und APIs
| Dimension / Kennzahl | | |
|---|---|---|
| Offizielle Domain | beaglesecurity.com | zerothreat.ai |
| Preismodell | Freemium, Kostenlose Testversion, Kostenpflichtig, Preise auf Anfrage | Kostenlos |
| Monatliche Besuche | 38.309 (38.309) | 29.304 (29.304) |
| MoM-Traffic-Delta | -21.318 (-35,8 %) | -3711 (-11,2 %) |
|---|
| Primärmarkt und Anteil | 🇮🇳 Indien (15,9 %) | 🇺🇸 Vereinigte Staaten (37,9 %) |
|---|
| Direkte Besuche / Monat | 8395 | 11.815 |
|---|
| Nutzerbewertung | 4,4 | 4,2 |
|---|
| Unterstützte Plattformen | Website | Website |
|---|
Agentisches KI-Pentesting für Web-Apps, APIs und GraphQL
Eine mit über 350.000 Workflows trainierte KI führt menschenähnliche, mehrstufige Angriffsketten gegen Web-Apps, APIs und GraphQL-Dienste aus.
Sie bringen der KI Ihre individuellen Abläufe durch Aufzeichnung einer echten Sitzung bei, sodass Tests echte Logik prüfen und nicht nur Links crawlen.
Befunde sind mit CVSS und OWASP bewertet und bis auf Stack- und Codeebene erklärt – mit Schritt-für-Schritt-Anleitung statt roher Alarmlisten.
Schwachstellen nach Jira, Azure Boards, Slack, Teams oder Postman pushen oder Tests aus der CI/CD-Pipeline beim Release auslösen.
Kontinuierliches KI-gestütztes Pentesting für Web-Apps und APIs
Führen Sie unbegrenzte automatisierte Penetrationstests pro Ziel aus, die echte Angreifer-Workflows nachahmen und ausnutzbare Pfade validieren statt nur CVEs zu markieren.
Scannen Sie authentifizierte Bereiche, Geschäftslogik und Zugriffskontrollen, um BOLA-, IDOR- und Rechteausweitungsfehler aufzudecken, die Signaturscanner übersehen.
Decken Sie REST-, GraphQL-, SOAP- und gRPC-Schnittstellen ab, entdecken Sie Shadow-APIs und erkennen Sie API-spezifische Angriffsmuster.
Testen Sie Live-Produktionsanwendungen ohne Unterbrechung und verlassen Sie sich auf auditfähige Nachweise sowie kontinuierliches Mapping zu DSGVO, ISO 27001, PCI-DSS und HIPAA.
All-in-One-AppSec-Plattform, die Schwachstellen findet und automatisch behebt

ProjectDiscovery Neo is an AI-driven offensive security platform that continuously maps your external, internal, cloud and code attack surface, replays every finding against the live target to prove exploitability, then opens fix pull requests and regression tests. It is built by the team behind nuclei, subfinder and httpx.
KI-gestützte Testplattform für Web, Mobile, API und Desktop

Angreifergeleitete KI-Sicherheitstests und Red Teaming

AI-native Offensive Security: kontinuierliches Red Teaming, Whitebox-Pentests und PR-Review

testRigor is an agentic AI test automation platform that lets you build end-to-end tests in plain English instead of code. It covers web, mobile, native desktop, API, email, SMS, phone calls, 2FA, and mainframe testing, includes free unlimited Generative AI, and self-heals tests so manual QA teams can automate without engineering help.
Agentischer KI-QA-Engineer für Web, iOS und Android

KI-Testplattform für den gesamten Softwaretest-Lebenszyklus
Autonome KI-QA-Agenten, die deine Web- und Mobile-App bei jedem Pull Request verifizieren

Equixly is an autonomous penetration testing and AI red teaming platform. Powered by its own AI model, it continuously tests web applications, APIs, GenAI apps, and MCP servers, validating exploits and chaining findings into real attack paths.

Autonome KI-Sicherheitsmitarbeiter für kontinuierliches Pentesting

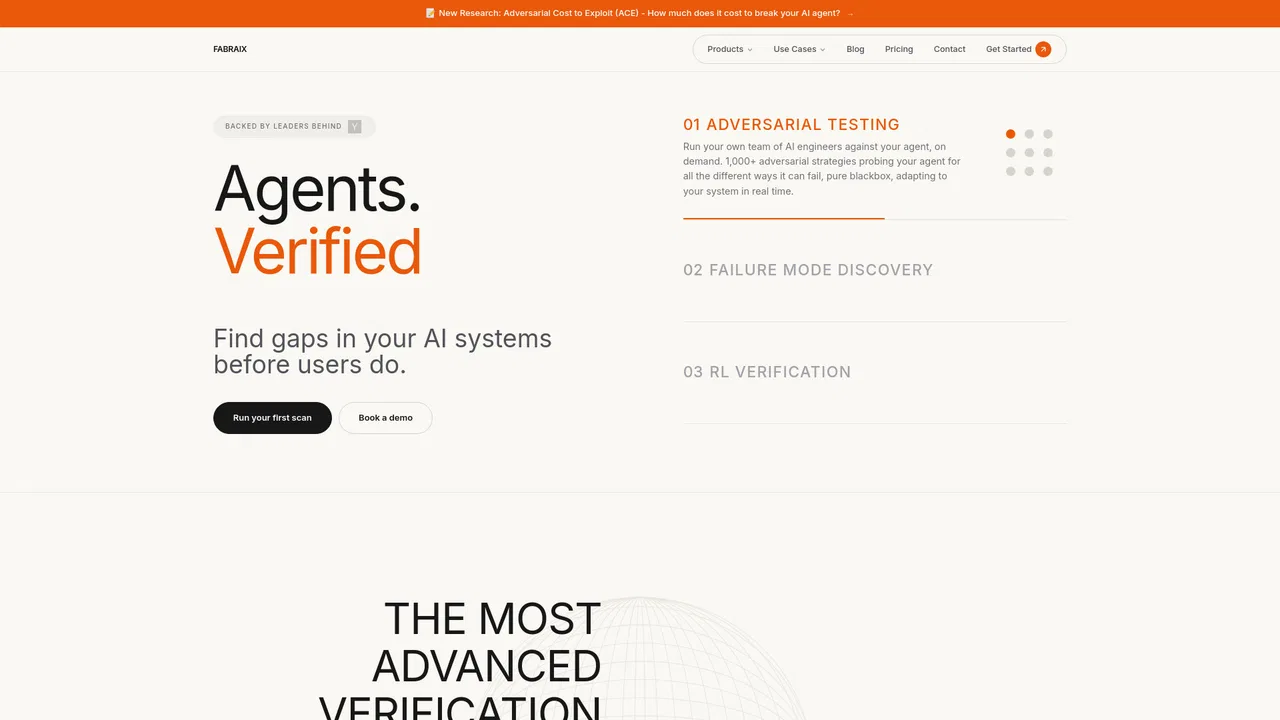
Fabraix is an adversarial-verification platform built around Nyx, an autonomous red-teaming harness that probes your AI agents across security, logic and alignment. It is pure blackbox — no integration or internal access required — and runs 10,000+ adaptive, multi-turn attack strategies in massively parallel simulations to surface the failure modes static benchmarks miss.
All-in-One-AppSec-Plattform, die Schwachstellen findet und automatisch behebt
ProjectDiscovery Neo is an AI-driven offensive security platform that continuously maps your external, internal, cloud and code attack surface, replays every finding against the live target to prove exploitability, then opens fix pull requests and regression tests. It is built by the team behind nuclei, subfinder and httpx.
Angreifergeleitete KI-Sicherheitstests und Red Teaming
testRigor is an agentic AI test automation platform that lets you build end-to-end tests in plain English instead of code. It covers web, mobile, native desktop, API, email, SMS, phone calls, 2FA, and mainframe testing, includes free unlimited Generative AI, and self-heals tests so manual QA teams can automate without engineering help.
Agentischer KI-QA-Engineer für Web, iOS und Android
KI-Testplattform für den gesamten Softwaretest-Lebenszyklus
Autonome KI-QA-Agenten, die deine Web- und Mobile-App bei jedem Pull Request verifizieren
Equixly is an autonomous penetration testing and AI red teaming platform. Powered by its own AI model, it continuously tests web applications, APIs, GenAI apps, and MCP servers, validating exploits and chaining findings into real attack paths.
Fabraix is an adversarial-verification platform built around Nyx, an autonomous red-teaming harness that probes your AI agents across security, logic and alignment. It is pure blackbox — no integration or internal access required — and runs 10,000+ adaptive, multi-turn attack strategies in massively parallel simulations to surface the failure modes static benchmarks miss.