01
KaneAIOffiziell
901.340/Monat
GenAI-nativer E2E-QA-Agent, der Tests in natürlicher Sprache plant, schreibt und heilt
AI AgentRedaktionswert: 4.5Freemium, Kostenpflichtig, Preise auf Anfrage+13,2 %
Donely verzeichnet 10.995 monatliche Besuche mit -0,9 % Wachstum gegenüber dem Vormonat und einem Preismodell „Freemium, Kostenlose Testversion“. Equixly verzeichnet 13.245 monatliche Besuche mit -34,3 % Wachstum und einem Preismodell „Preise auf Anfrage“.

Autonome KI-Sicherheitsmitarbeiter für kontinuierliches Pentesting

Equixly is an autonomous penetration testing and AI red teaming platform. Powered by its own AI model, it continuously tests web applications, APIs, GenAI apps, and MCP servers, validating exploits and chaining findings into real attack paths.
| Dimension / Kennzahl | | |
|---|---|---|
| Offizielle Domain | donely.ai | equixly.com |
| Preismodell | Freemium, Kostenlose Testversion | Preise auf Anfrage |
| Monatliche Besuche | 10.995 (10.995) | 13.245 (13.245) |
| MoM-Traffic-Delta | -104 (-0,9 %) | -6917 (-34,3 %) |
| Primärmarkt und Anteil | 🇺🇸 Vereinigte Staaten (28,8 %) | 🇺🇸 Vereinigte Staaten (30,9 %) |
| Direkte Besuche / Monat | 4554 | 5289 |
| Nutzerbewertung | 4,2 | 4,1 |
| Unterstützte Plattformen | Website | Website |
Autonome KI-Sicherheitsmitarbeiter für kontinuierliches Pentesting
Jedes gemeldete Problem enthält einen reproduzierbaren Proof of Concept, Request-/Response-Details und eine Einschätzung des Auswirkungsradius.
Tausende kurzlebige Agenten verfolgen unter einem persistenten Koordinator je ein fokussiertes Angriffsziel.
Ein steuerbarer Headless-Browser plus Burp, ZAP, Nuclei, sqlmap, Semgrep und eigene Payloads.
Aus der CI bei jedem Merge auslösen oder kontinuierlich gegen Staging und Produktion laufen lassen.
Equixly is an autonomous penetration testing and AI red teaming platform. Powered by its own AI model, it continuously tests web applications, APIs, GenAI apps, and MCP servers, validating exploits and chaining findings into real attack paths.
Discovery, Attacker, Evaluator, and Orchestrator agents map a target, attempt exploits, verify what actually worked, and chain findings into real attack paths.
Every finding passes a proof-of-exploit gate, so reports focus on vulnerabilities an attacker can genuinely reach instead of unvalidated alerts.
Test web apps, APIs, GenAI and LLM applications, and MCP servers across one platform, with coverage that scales from a single app to a portfolio.
Trigger testing from your pipeline so applications are re-tested as they change, with no separate charge tied to test frequency.
GenAI-nativer E2E-QA-Agent, der Tests in natürlicher Sprache plant, schreibt und heilt

Kostenlos / Open SourceAll-in-One-AppSec-Plattform, die Schwachstellen findet und automatisch behebt
Kostenlos / Open SourceAll-in-One-AppSec-Plattform, die Schwachstellen findet und automatisch behebt

ProjectDiscovery Neo is an AI-driven offensive security platform that continuously maps your external, internal, cloud and code attack surface, replays every finding against the live target to prove exploitability, then opens fix pull requests and regression tests. It is built by the team behind nuclei, subfinder and httpx.
ProjectDiscovery Neo is an AI-driven offensive security platform that continuously maps your external, internal, cloud and code attack surface, replays every finding against the live target to prove exploitability, then opens fix pull requests and regression tests. It is built by the team behind nuclei, subfinder and httpx.

Angreifergeleitete KI-Sicherheitstests und Red Teaming
Angreifergeleitete KI-Sicherheitstests und Red Teaming

Kostenlos / Open SourceAI-native Offensive Security: kontinuierliches Red Teaming, Whitebox-Pentests und PR-Review

Kostenlos / Open SourceLLM-Evaluation, Observability und Red Teaming unternehmensweit standardisieren
Kostenlos / Open SourceLLM-Evaluation, Observability und Red Teaming unternehmensweit standardisieren

Kostenlos / Open SourceAgentisches KI-Pentesting für Web-Apps, APIs und GraphQL
Kostenlos / Open SourceAgentisches KI-Pentesting für Web-Apps, APIs und GraphQL
Kostenlos / Open SourceCloud-Sicherheitsrisiken mit KI-gestützten Workflows finden, priorisieren und beheben
Kostenlos / Open SourceCloud-Sicherheitsrisiken mit KI-gestützten Workflows finden, priorisieren und beheben

Kostenlos / Open SourceAutonome KI-QA-Agenten, die deine Web- und Mobile-App bei jedem Pull Request verifizieren
Kostenlos / Open SourceAutonome KI-QA-Agenten, die deine Web- und Mobile-App bei jedem Pull Request verifizieren
Kostenlos / Open SourceKontinuierliches KI-gestütztes Pentesting für Web-Apps und APIs
Kostenlos / Open SourceKontinuierliches KI-gestütztes Pentesting für Web-Apps und APIs

Kostenlos / Open SourceDie Sicherheitsschicht für Sprach- und Chat-Agenten: testen, red teamen, überwachen
Kostenlos / Open SourceDie Sicherheitsschicht für Sprach- und Chat-Agenten: testen, red teamen, überwachen

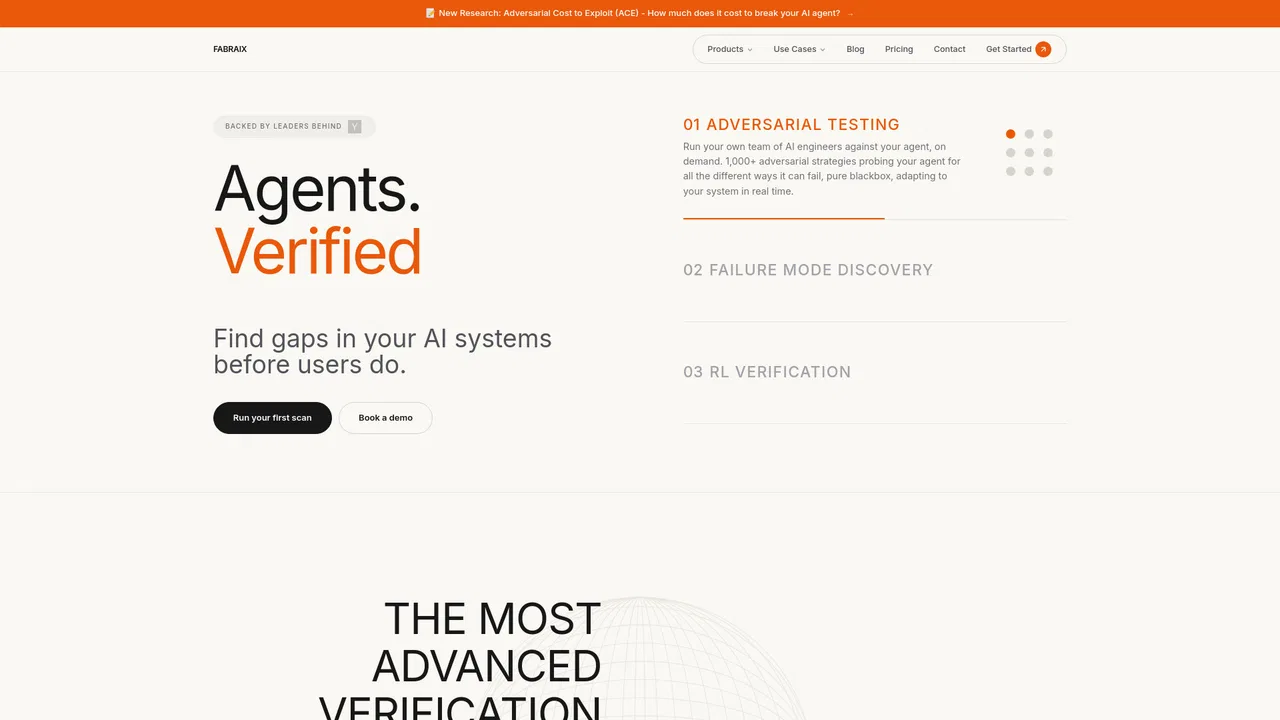
Kostenlos / Open SourceFabraix is an adversarial-verification platform built around Nyx, an autonomous red-teaming harness that probes your AI agents across security, logic and alignment. It is pure blackbox — no integration or internal access required — and runs 10,000+ adaptive, multi-turn attack strategies in massively parallel simulations to surface the failure modes static benchmarks miss.
Kostenlos / Open SourceFabraix is an adversarial-verification platform built around Nyx, an autonomous red-teaming harness that probes your AI agents across security, logic and alignment. It is pure blackbox — no integration or internal access required — and runs 10,000+ adaptive, multi-turn attack strategies in massively parallel simulations to surface the failure modes static benchmarks miss.