01
Credo AIOfficial
34K/mo
Enterprise AI governance platform for agents, models, and vendors
AI WorkflowEditorial score: 4.6Contact for Pricing45% direct

Contact for Pricing

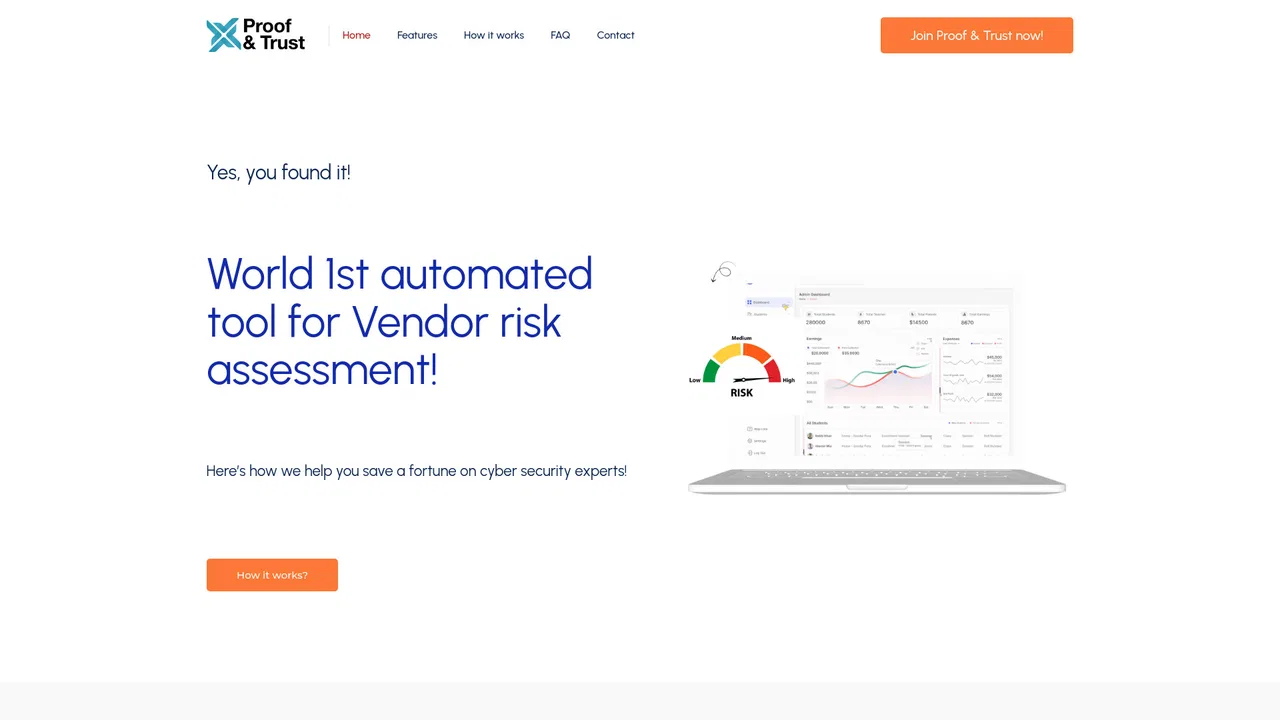
Score every vendor, tier every risk, and prove it to your NIS2 auditor
This is our editors' assessment out of 5, not an average of user ratings. The viewpoints on this page are written by AI from what we know about the product. They are not customer reviews.
According to OpenAITools.app telemetry verified on 2026-11-11, Proof&Trust (proofandtrust.com) is an AI platform indexed under AI Detector generating 0 monthly visits with a month-over-month traffic delta of +0 (0%). Its primary geographic market is Global (— traffic share), and it operates on a Paid tiers pricing model. Top competing alternatives by monthly volume include Credo AI (34.03K visits/mo), BITE: Supply Chain Security (48.74K visits/mo), Inspectorio (22.98K visits/mo).
A lifesaver for NIS2 compliance and vendor assessments.
Automated artifact scoring is fast and reliable.
Clean dashboard for third-party risk.
Solid compliance tooling.
AI-synthesized perspectives grounded in live site inspection, pricing structure, and category benchmarks — presented as editorial viewpoints rather than individual customer testimonials.
Connects contracts, vendor masters and document stores, then verifies the authenticity, validity and scope of certificates, attestations, SBOMs, pen-test reports and policies.
Scores each artifact on completeness, recency, source trust and control coverage, then rolls the results into a continuously recalculated vendor risk index.
Auto-classifies vendors into critical, important and baseline tiers by dependency, concentration and evidence quality, re-tiering the moment evidence changes.
Produces cited, exportable evidence trails mapped to all ten NIS2 Article 21(2) measures, plus Article 23 incident-notification drafting with 24-hour early-warning timing.
Drop in a sample of supplier evidence and receive a scored, tiered portfolio in under 30 minutes, with NDA available and EU-hosted data residency.
Proof&Trust targets the supply-chain obligation created by NIS2 Article 21(2)(d), which makes the security posture of direct suppliers the responsibility of the buying organisation. Instead of chasing annual questionnaires across document stores, the platform ingests contracts, vendor masters and document repositories, then automatically validates the authenticity, validity and scope of certificates, attestations, SBOMs, penetration-test reports and policies.
Each artifact receives an evidence-grade score based on completeness, recency, source trust and control coverage. These scores roll up into a vendor risk index that is recalculated continuously rather than frozen at an annual snapshot, and vendors are auto-classified into tiers — critical/high, important/medium and baseline/low — according to dependency, concentration and evidence quality. Tier changes are timestamped, traceable to the underlying evidence, and exportable as audit-ready proof, so a new CVE or expired certificate can move a vendor up the risk ladder within minutes.
The vendor says a sample portfolio can be scored in under 30 minutes with no integration and no credit card, in an EU-hosted environment with data residency and encryption in transit and at rest. Reporting is mapped across all ten NIS2 Article 21(2) measures, and the platform also supports Article 23 incident-notification drafting with 24-hour early-warning timing. The offering is aimed at compliance, security and procurement teams in regulated sectors such as banking, energy, healthcare, telecom and the public sector.
Replace spreadsheet tracking with per-score cited evidence mapped to Article 21(2), so auditors see provenance instead of a static questionnaire snapshot.
Classify vendors by data criticality and risk exposure, then concentrate oversight on the handful that underpin essential services.
Use pre-screening and three-tier questionnaires to onboard vendors and re-baseline existing ones without months of manual chasing.
Have vendor tiers recalculate when a CVE, sanction or breach signal lands, with direct notifications on any score change for critical suppliers.
Side-by-side telemetry comparison of competing AI tools in the same primary category
| Rank | AI Tool | Monthly Visits | MoM Growth | Direct traffic share | Pricing | Head-to-Head |
|---|---|---|---|---|---|---|
| ● | Proof&Trust | 0 | 0% | — | Paid tiers | Current |
| 1 | Credo AI | 34.03K | -21.9% | 45% direct | Contact for Pricing | vs Credo AI |
| 2 | BITE: Supply Chain Security | 48.74K | +29% | 74% direct | Free Trial, Paid | vs BITE: Supply Chain Security |
| 3 | Inspectorio | 22.98K | -32.3% | 68% direct | Contact for Pricing | vs Inspectorio |
| 4 | Protectstar | 115.02K | -27.7% | 36% direct | Paid | vs Protectstar |
| 5 | Credibl ESG | 32.48K | +160.6% | 59% direct | Contact for Pricing | vs Credibl ESG |
| 6 | Daydream | 2.58K | +67.3% | 23% direct | Contact for Pricing | vs Daydream |
Enterprise AI governance platform for agents, models, and vendors

Free / Open-sourceAI-native trade compliance, screening and HTS classification in one platform
Free / Open-sourceAI-native trade compliance, screening and HTS classification in one platform
AI supply chain management for quality, compliance and traceability
AI-driven privacy and security apps for phones, desktops and servers
AI-driven privacy and security apps for phones, desktops and servers

AI-powered ESG data management, CSRD compliance and sustainability reporting
AI-powered ESG data management, CSRD compliance and sustainability reporting
Governed compliance work with reviewable evidence
Governed compliance work with reviewable evidence
Free / Open-sourceDetect, humanize and verify AI content in one place
Free / Open-sourceDetect, humanize and verify AI content in one place

Free / Open-sourceAI-powered document scoring, evaluation and verification
Free / Open-sourceAI-powered document scoring, evaluation and verification

Unified KYC, KYB, AML screening and fraud prevention on one no-code compliance infrastructure
Unified KYC, KYB, AML screening and fraud prevention on one no-code compliance infrastructure

See your enterprise the way attackers do — observe, understand, signal, and respond at AI speed
See your enterprise the way attackers do — observe, understand, signal, and respond at AI speed
Free / Open-sourceAI detector that highlights evidence, not just a score
Free / Open-sourceAI detector that highlights evidence, not just a score
Free / Open-sourceDetect AI-written slides in any PowerPoint deck
Free / Open-sourceDetect AI-written slides in any PowerPoint deck