01
757.5K/mo
All-in-one AppSec platform that finds and auto-fixes vulnerabilities
AI Code ReviewEditorial score: 4.4Freemium+9.6%

757.5K/mo+9.6%
All-in-one AppSec platform that finds and auto-fixes vulnerabilities
Freemium
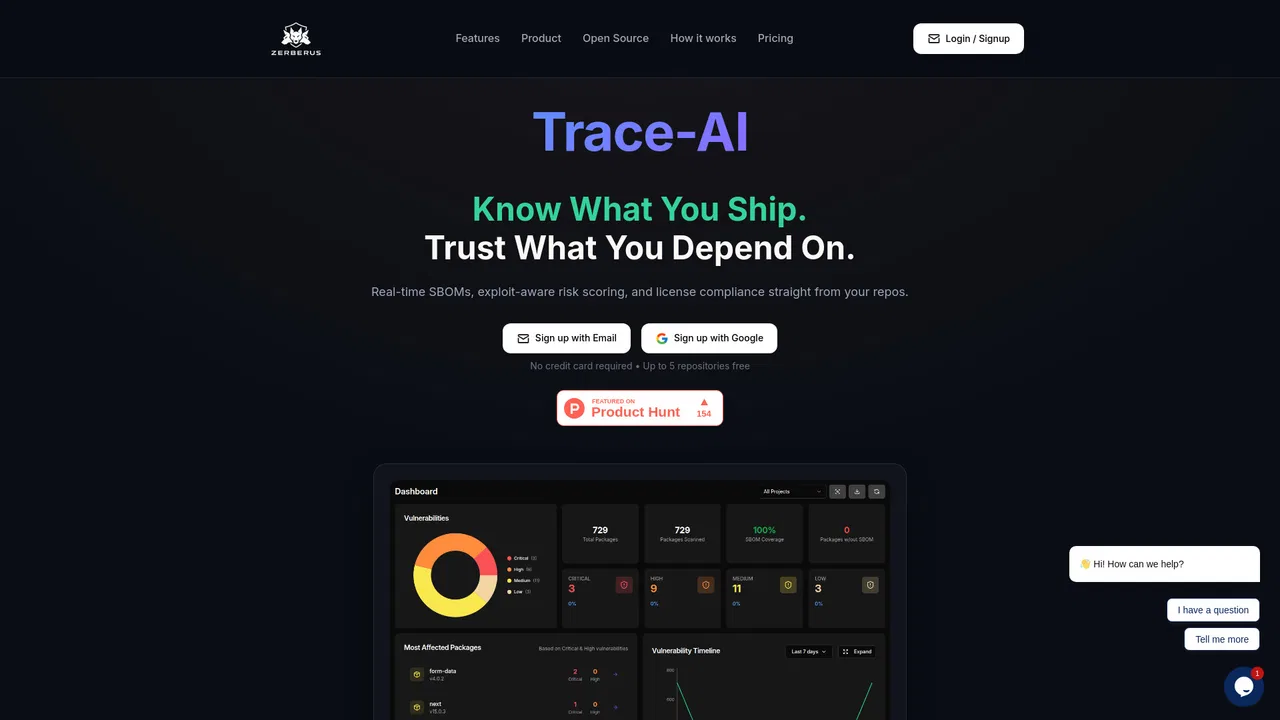
Know what you ship — real-time SBOMs and exploit-aware supply-chain security
This is our editors' assessment out of 5, not an average of user ratings. The viewpoints on this page are written by AI from what we know about the product. They are not customer reviews.
According to OpenAITools.app telemetry verified on 2026-11-11, Trace-AI (trace-ai.dev) is an AI platform indexed under AI Developer Tools generating 0 monthly visits with a month-over-month traffic delta of -370 (-100%). Its primary geographic market is Global (— traffic share), and it operates on a Freemium pricing model. Top competing alternatives by monthly volume include Aikido Security (757.49K visits/mo), Beagle Security (38.31K visits/mo), Detecting-AI.com (505.15K visits/mo).
Finally an SBOM tool that doesn't spam false positives every five minutes.
hooked it to our main gitlab instance and it just works.
clean UI and fast scans
pricing gets steep past the free tier though
AI-synthesized perspectives grounded in live site inspection, pricing structure, and category benchmarks — presented as editorial viewpoints rather than individual customer testimonials.
Produces accurate CycloneDX and SPDX software bills of materials from CI, continuously tracking both direct and transitive dependencies.
Moves beyond raw CVE dumps by prioritizing vulnerabilities that have known exploits in the wild and providing full context for remediation.
Identifies GPL, LGPL and other copyleft licenses instantly, with a policy library to avoid surprises during enterprise or legal review.
Tracks APIs, SDKs, SLA expiry and breach history alongside code dependencies so third-party risk is visible in one place.
Maps SBOM data to ISO 27001, SOC 2, PCI-DSS, HIPAA and GDPR checks and exports CycloneDX, SPDX or JSON reports for auditors.
Trace-AI answers a deceptively hard question: what is actually inside the software you ship? By connecting to a GitHub or GitLab repository, it builds a continuously updated Software Bill of Materials in CycloneDX or SPDX format, covering both direct and transitive dependencies. Because the SBOM refreshes as code evolves, teams always work from a current inventory instead of a stale snapshot.
Rather than dumping every CVE into a dashboard, Trace-AI applies exploit-aware risk scoring. It cross-references threat intelligence so that vulnerabilities with known exploits in the wild surface first, while low-signal alerts stay out of the way. Alongside vulnerability data, the platform tracks license distribution — flagging copyleft licenses such as GPL and LGPL — and monitors vendors, APIs, SDKs and SLA expiry so that third-party risk lives in the same view as code risk.
The product is built with transparency in mind. Its classification logic, policy-as-code checks and risk-scoring configuration are published as an open-source model (ZSBOM) so security teams can audit or fork the rules. Trace-AI is offered on a freemium basis with the first five repositories free, and exports evidence mapped to frameworks like ISO 27001 and SOC 2 for audit readiness.
Replace overwhelming CVE lists with a ranked view of vulnerabilities that are actually exploitable, so remediation time is spent where it counts.
Wire Trace-AI into GitHub or GitLab so every build produces an up-to-date SBOM and a live security posture dashboard.
Export policy-as-code evidence mapped to ISO 27001 and SOC 2 controls, reducing spreadsheet-driven audit prep.
Monitor APIs, SDKs, SLA expiry and breach history to keep vendor risk in the same workflow as dependency risk.
Side-by-side telemetry comparison of competing AI tools in the same primary category
| Rank | AI Tool | Monthly Visits | MoM Growth | Direct traffic share | Pricing | Head-to-Head |
|---|---|---|---|---|---|---|
| ● | Trace-AI | 0 | -100% | — | Freemium | Current |
| 1 | Aikido Security | 757.49K | +9.6% | 40% direct | Freemium | vs Aikido Security |
| 2 | Beagle Security | 38.31K | -35.8% | 22% direct | Freemium, Free Trial, Paid, Contact for Pricing | vs Beagle Security |
| 3 | Detecting-AI.com | 505.15K | +493% | 15% direct | Freemium, Paid | vs Detecting-AI.com |
| 4 | Binarly | 5.81K | -23.7% | 39% direct | Contact for Pricing | vs Binarly |
| 5 | Confident AI | 83.4K | -3.3% | 35% direct | Freemium, Paid, Contact for Pricing | vs Confident AI |
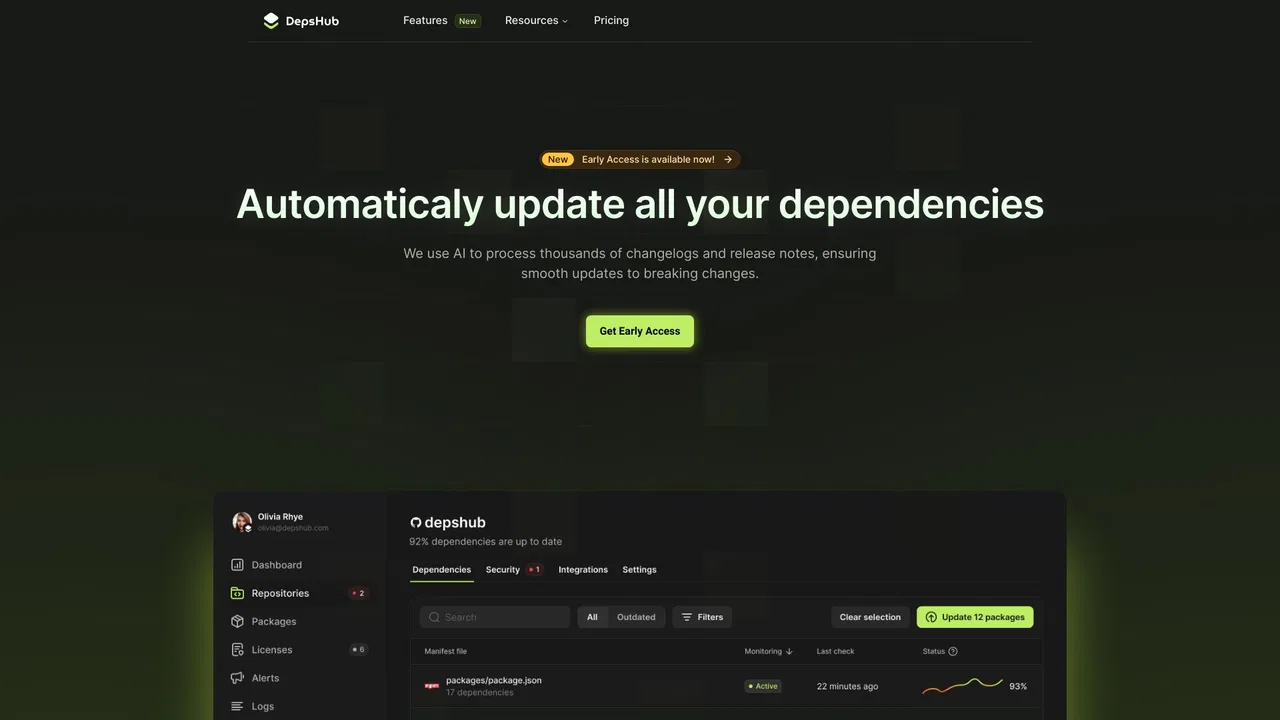
| 6 | DepsHub | 2.74K | +27.7% | 39% direct | Freemium | vs DepsHub |
All-in-one AppSec platform that finds and auto-fixes vulnerabilities
All-in-one AppSec platform that finds and auto-fixes vulnerabilities

Agentic AI penetration testing for web apps, APIs and GraphQL
AI detector that highlights evidence, not just a score
AI detector that highlights evidence, not just a score

Binary-level security for the software and firmware you ship

Standardize LLM evaluation, observability, and red teaming across your whole org
Standardize LLM evaluation, observability, and red teaming across your whole org
Automated dependency updates, license compliance, and security scanning for your repos
Automated dependency updates, license compliance, and security scanning for your repos

Attack-led AI security testing and red teaming
Attack-led AI security testing and red teaming
Continuous AI-powered pentesting for web apps and APIs
Continuous AI-powered pentesting for web apps and APIs

Generative AI security for multi-cloud apps — embedded where developers work
Generative AI security for multi-cloud apps — embedded where developers work

Free / Open-sourceAgent observability, evaluation, and continuous improvement for production AI
Free / Open-sourceAgent observability, evaluation, and continuous improvement for production AI
Free / Open-sourceOpen-source model and dataset hub with one-click online demos
Free / Open-sourceOpen-source model and dataset hub with one-click online demos
AI detection and writing verification built for schools and editors